Independent consultancy specialising in SME cybersecurity • NIS2
Your cybersecurity,
a lasting advantage.
NIS2 raises cyber requirements, including for SMEs, directly or through their clients.
LINARIS turns these challenges into practical actions to protect your business,
retain contracts and win new markets.
Manufacturing • E‑commerce • Logistics • Finance • Services
Method aligned with the ReCyF (ANSSI)
Paris • Île-de-France • France
The challenge
Cybersecurity is being imposed on you, and you don’t control it.
Hard to know what really applies to you, what is expected of you, where to start and how far to go.
Advice is everywhere. Harder to find advice that speaks to business leaders.
Often too technical, too generic, or written for IT people and lawyers.
You are short on time. Cyber risk is not.
Lost contract, refused insurance, production at a standstill: inaction can be costly.
LINARIS builds a roadmap with you, sized to your business, then supports you through implementation and follow-up.
Getting started
Take stock, free and with no commitment.
01 · 1 minute
Find your situation
Three typical situations: find the one that matches your business.
02 · 45 minutes, free
Review your situation with a LINARIS specialist
A remote conversation focused on your business.
03 · after the review
Receive your written summary
Where you stand and your next steps.
To go further, ask for our SME Cyber Assessment.
Your situation
NIS2: mandatory for some, the benchmark for all.
Choose the situation that matches yours.
My company is in scope of NIS2
Make NIS2 the foundation of your cybersecurity.
NIS2 makes you accountable as a business leader. With us, you know what applies to you, where to start, and you keep the evidence.
How we help ↻
My company is in scope of NIS2
LINARIS helps you:
- turn NIS2 into concrete measures, without jargon;
- measure your gaps against NIS2 requirements;
- assess your cyber risks;
- build a detailed roadmap, at your own pace;
- implement the necessary measures and keep evidence of them.
← Back
My clients or my insurer require proof of my cybersecurity
Meet your clients’ requirements with confidence.
Questionnaires, contract clauses, audits, insurance conditions: a commitment you haven’t weighed up can cost you a contract. You control what you declare, and you can prove it.
How we help ↻
My clients or my insurer require proof of my cybersecurity
LINARIS helps you:
- understand what your client or insurer actually expects;
- measure your gaps and fix first the weaknesses that expose you most;
- structure your security measures and the evidence behind them;
- answer security questionnaires consistently, with supporting evidence.
← Back
I’m not in scope, but I want to get ahead
Outside NIS2 scope does not mean outside risk.
No obligations today, but the same risks. We adapt the ReCyF, ANSSI’s NIS2 framework, to your size and resources.
How we help ↻
I’m not in scope, but I want to get ahead
LINARIS helps you:
- identify your main cyber risks;
- assess your current level of security;
- build a realistic roadmap, within your means;
- implement the necessary actions, without buying more than you need.
← Back
Whatever your situation, NIS2 may be the trigger. Cybersecurity remains the goal.
Our founders
Cyber, risk, governance: excellence for your SME.
Complementary profiles on every level: information security and risk analysis, manufacturing and finance, SMEs and large corporations.
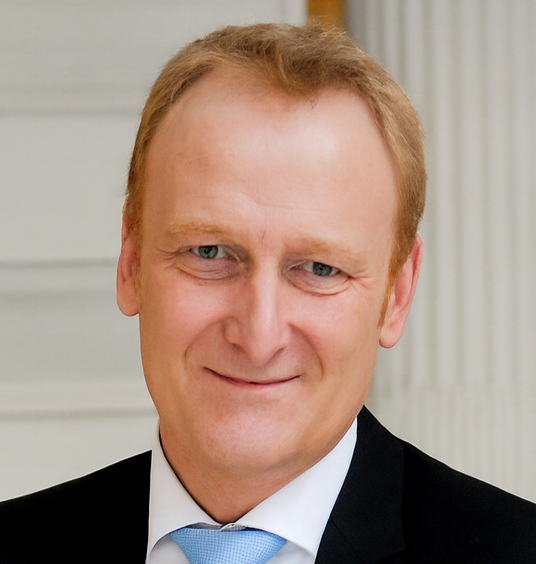
Stéphane Hivert
Operational Cyber Specialist
Over more than 25 years, in France and abroad, I have worked exclusively in SMEs and start-ups: as a plant manager, an executive, then a consultant. I practised cybersecurity there as a business leader, to keep operations running.
At Lazada, an e-commerce start-up since acquired by Alibaba, I built warehouses with cybersecurity in the plans from day one, because a paralysed warehouse delivers to no one. In manufacturing, I secured every project exposed to digital systems, because a stopped production line is revenue that stops coming in.
To me, cybersecurity is a foundation for the long term, not a fix. Yet an SME, short of time, resources and guidance, fixes things after the fact. That is the gap I chose to fill.
I start from your operational reality to identify the risks that really matter and help you act, within your means.
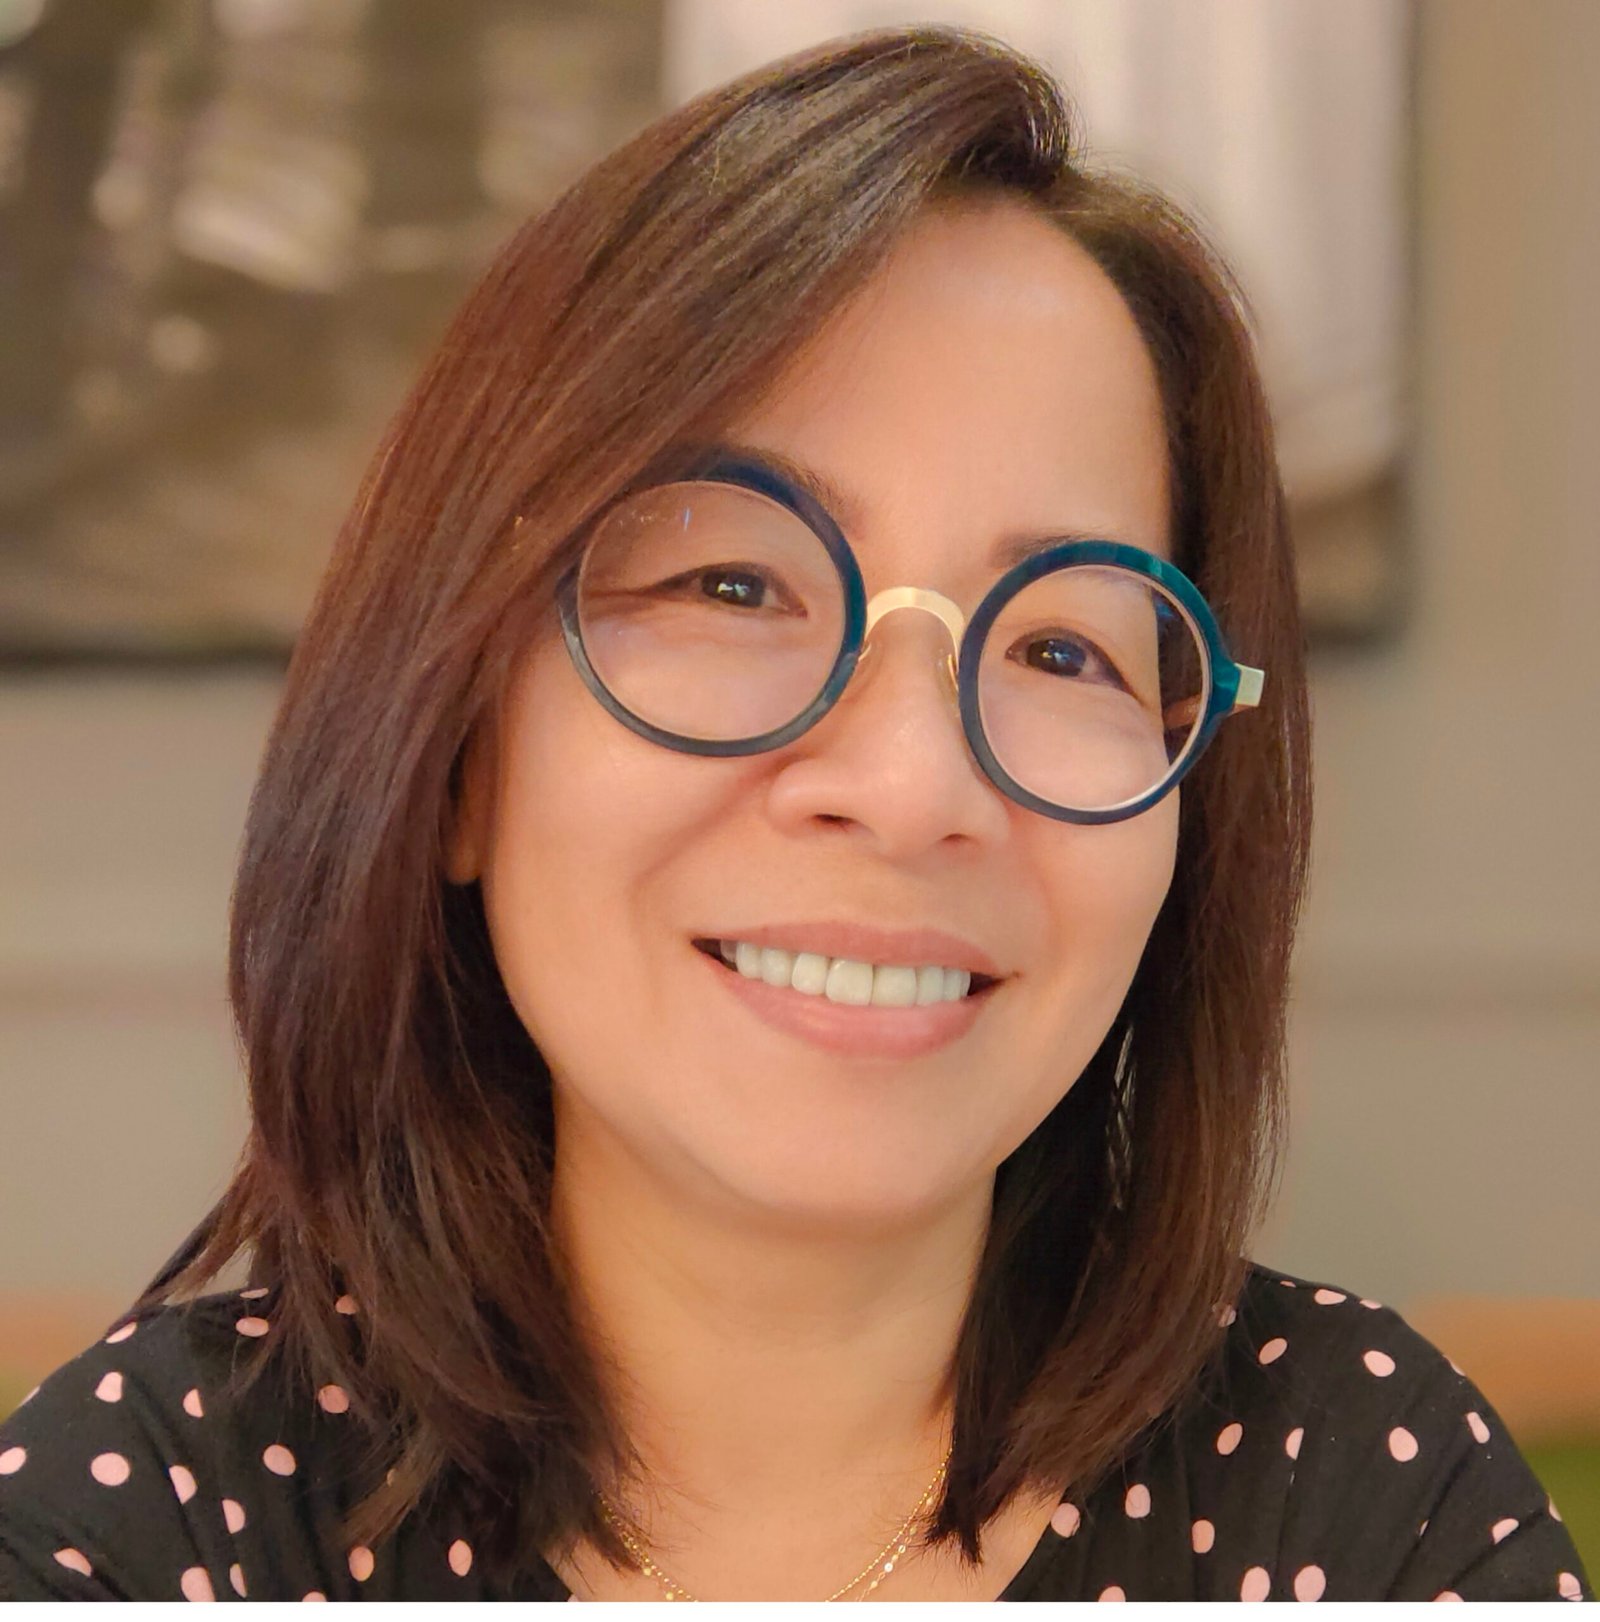
Lai Ly
Cyber Governance Specialist
I spent more than 25 years in international finance, one of the most heavily regulated sectors.
Risk analysis is my profession. At S&P Global Ratings and Amundi, I led teams specialising in credit risk and ESG risk analysis.
Whenever I encountered a new type of risk, I developed the methodology needed to assess it.
I have also assessed governance practices and worked directly in governance, the G in ESG. I know how to distinguish what actually works from what exists only on paper.
Today, SMEs must also manage cyber risks and meet growing requirements, without having the specialised teams available to large corporations.
At LINARIS, I bring this combined experience in risk analysis and governance to help SMEs understand and implement cybersecurity and regulatory requirements, applying the rigour of large corporations without their complexity.
With us, your cybersecurity is in the hands of senior specialists.
How we support you
An assessment first. The rest, only if it serves you.
Every company is different.
So is the support you get.
01
SME Cyber Assessment
Aligned with the ReCyF, the NIS2 framework published by ANSSI, France’s national cybersecurity agency, in March 2026.
You know where you stand. You receive:
- an analysis of your cyber risks, across your whole business;
- a measure of your gaps against the ReCyF;
- a detailed roadmap to decide on.
Targeted interviews and an on-site visit, without disrupting your business.
02
Implementation Support
Building on your action plan, we develop a roadmap with you and support its implementation across the four ReCyF domains. For example:
- Governance: train business leaders, raise staff awareness and manage third-party cyber risks.
- Protection: define access rights, isolate sensitive systems and secure connections.
- Defence: organise security monitoring, assign responsibilities, prepare incident response procedures.
- Resilience: establish recovery priorities, prepare crisis management procedures, test business continuity plans.
We coordinate the teams involved, help overcome obstacles and verify progress.
03
Ongoing support
Your business evolves, and so do its cyber risks. We check that your security measures remain effective, update your risk assessments and help you adjust your priorities.
Our fees are fixed for an agreed scope of work and defined with you before any commitment.
Our insights
NIS2 and SME cyber: the text, the field, without the drama.
Practical guide · in French
NIS2 and SMEs: a practical guide for business leaders
Are you in scope, what must you do, what do you risk: the text’s answers, situation by situation.
Lai Ly and Stéphane Hivert · updated September 2026
NIS2 and SMEs #1 · in French
Management accountability: what the text actually says
Fines, bans from management: what the Directive really requires of you, and what it does not.
Lai Ly · updated October 2026
Field survey
Cybersecurity in manufacturing SMEs: 3 blind spots revealed by our survey
25 out of 30 business leaders don’t know what NIS2 contains. What we found on the ground, and how to respond.
Stéphane Hivert · 30 SMEs surveyed in March 2026
What sets us apart
Three reasons to work with LINARIS
From one business leader to another
Our cybersecurity recommendations combine technical, operational and organisational considerations. They are clear and practical to implement.
No hidden sales agenda
Our cybersecurity recommendations serve your business, not the sale of software or hardware.
A method aligned with ANSSI and ReCyF
We draw on Directive (EU) 2022/2555 and ANSSI’s ReCyF framework to help you make sound, well-justified cybersecurity decisions.
An independent view, the rigour of ANSSI methodologies and the experience of business leaders.
FAQ
Frequently asked questions: SME cybersecurity and NIS2
How does the free 45-minute cyber review ?
It is a remote conversation with a LINARIS specialist. We go over your business, your organisation and your main digital dependencies. We also review how prepared you are in cybersecurity for the requirements of your clients, your insurer or NIS2, depending on your situation. You receive an initial estimate of your level of readiness and the steps to consider. It is free and with no commitment. The SME Cyber Assessment is a separate engagement, which we only offer if it is useful to you.
You are not lawyers. How do you help me respond to cybersecurity questionnaires or my client’s cyber clause?
We help you understand exactly what your clients require in cybersecurity, particularly in supplier security questionnaires, identify your gaps and priority actions, then prepare consistent, well-supported answers. To assess the legal implications of a questionnaire answer that binds you, or of a cyber clause, we recommend consulting your lawyer.
My company is not subject to NIS2. Why prepare for it?
Because the NIS2 Directive is becoming the market benchmark for cybersecurity. Organisations subject to it must secure their supply chain and may pass their cyber requirements on to their suppliers. If you supply a client that is subject to NIS2, you may therefore be indirectly affected by its requirements. If not, you are outside its scope for now. But if you plan to expand into a sector covered by NIS2 or to work with a client subject to the Directive, it is wise to get ahead by aligning your cybersecurity practices with the relevant requirements.
What is the difference between my IT service provider and a cybersecurity consultancy?
We provide a specialised, independent perspective on SME cybersecurity that complements the work of your IT provider or IT department. Your IT teams manage the day-to-day performance, availability and maintenance of your systems. We assess cyber risks across your business, help you define appropriate measures and oversee their implementation. We coordinate the teams involved, extending beyond IT alone. Both areas of expertise complement each other and work together.
Can I handle NIS2 compliance on my own, with software?
Yes, provided you have the in-house expertise and time to select the right tool and manage your NIS2 compliance programme. Software can guide the process, help document practices and make progress easier to track. But decisions about budgets, organisational changes, team involvement and which risks to accept remain yours. We help you make decisions and take action: measures tailored to your NIS2 obligations, priorities based on your risks and resources, teams supported through implementation, and results verified and documented.
Contact
Book your free 45-minute Cyber review.
Clarify the cybersecurity requirements that apply to your business. Leave with an initial assessment of your situation and the next steps to consider. No obligation.
Book a time in our calendar
Calendar not showing? Call +33 9 85 00 19 31.
Cyber incident: +33 6 56 68 17 11
We will call you back within 24 business hours and can then respond as quickly as possible in Île-de-France: incident analysis, containment and recovery.
If you’re experiencing an active cyberattack, find immediate guidance at 17Cyber.gouv.fr, the French government’s cyber emergency service (in French).
LINARIS · Independent Cybersecurity Advisory for SMEs · Based in Versailles · On-site services across Île-de-France – Paris (75), Seine-et-Marne (77), Yvelines (78), Essonne (91), Hauts-de-Seine (92), Seine-Saint-Denis (93), Val-de-Marne (94), Val-d’Oise (95) – and in Eure (27), Eure-et-Loir (28) and Orne (61). Services elsewhere in France on a case-by-case basis · On-site and remote consultations.