Independent consultancy specialising in SME cybersecurity • NIS2
Clear decisions for your cybersecurity.
Your clients ask, your insurer insists, NIS2 sets the standard. From one business leader to another, we translate these demands into concrete action.
50+ years of combined experience
Manufacturing • E‑commerce • Finance
Method aligned with the ReCyF (ANSSI)
Paris • Île-de-France • France
The challenge
Cybersecurity is being imposed on you, and you don’t control it.
Hard to know what really applies to you, what is expected of you, where to start and how far to go.
Advice is everywhere. None of it speaks to you, the business leader.
Often too technical, too generic, or written for IT people and lawyers.
You are short on time. Cyber risk is not.
Lost contract, refused insurance, production at a standstill : inaction can be costly.
LINARIS builds a roadmap with you, sized to your business, then supports you through implementation and follow-up.
Getting started
Take stock, free and with no commitment.
01 · 1 minute
Find your situation
Three typical situations : find the one that matches your business.
02 · 45 minutes, free
Review your situation with a LINARIS specialist
A remote conversation focused on your business.
03 · after the review
Receive your written summary
Where you stand and your next steps.
To go further, ask for our SME Cyber Assessment.
Your situation
NIS2 : mandatory for some, the benchmark for all.
Choose the situation that matches yours.
My company is in scope of NIS2
Make NIS2 the foundation of your cybersecurity.
NIS2 makes you accountable as a business leader. With us, you know what applies to you, where to start, and you keep the evidence.
How we help ↻
My company is in scope of NIS2
LINARIS helps you :
- turn NIS2 into concrete measures, without jargon ;
- measure your gaps against NIS2 requirements ;
- assess your cyber risks ;
- build a detailed roadmap, at your own pace ;
- implement the necessary measures and keep evidence of them.
← Back
My clients or my insurer require proof of my cybersecurity
Meet your clients’ requirements with confidence.
Questionnaires, contract clauses, audits, insurance conditions : a commitment you haven’t weighed up can cost you a contract. You control what you declare, and you can prove it.
How we help ↻
My clients or my insurer require proof of my cybersecurity
LINARIS helps you :
- understand what your client or insurer actually expects ;
- measure your gaps and fix first the weaknesses that expose you most ;
- structure your security measures and the evidence behind them ;
- answer security questionnaires consistently, with supporting evidence.
← Back
I’m not in scope, but I want to get ahead
Outside NIS2 scope does not mean outside risk.
No obligations today, but the same risks. We adapt the ReCyF, ANSSI’s NIS2 framework, to your size and resources.
How we help ↻
I’m not in scope, but I want to get ahead
LINARIS helps you :
- identify your main cyber risks ;
- assess your current level of security ;
- build a realistic roadmap, within your means ;
- implement the necessary actions, without buying more than you need.
← Back
Whatever your situation, NIS2 may be the trigger. Cybersecurity remains the goal.
Our founders
Cyber, risk, governance : excellence for your SME.
Complementary profiles on every level : information security and risk analysis, manufacturing and finance, SMEs and large corporations.
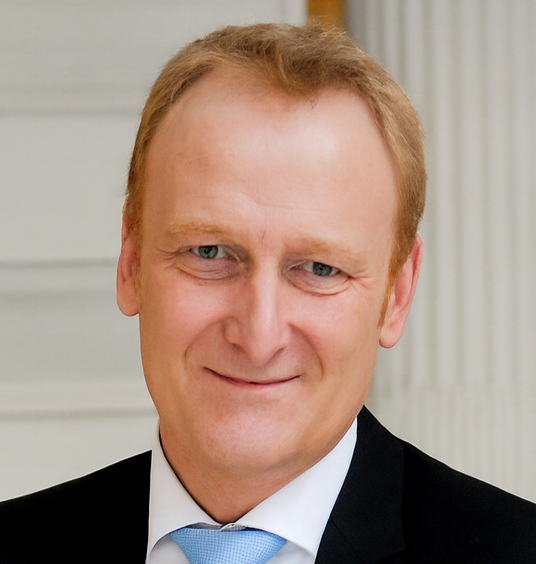
Stéphane Hivert
Operational Cyber Specialist
Over more than 25 years, in France and abroad, I have worked exclusively in SMEs and start-ups : as a plant manager, an executive, then a consultant. I practised cybersecurity there as a business leader, to keep operations running.
At Lazada, an e‑commerce start-up since acquired by Alibaba, I built warehouses with cybersecurity in the plans from day one, because a paralysed warehouse delivers to no one. In manufacturing, I secured every project exposed to digital systems, because a stopped production line is revenue that stops coming in.
To me, cybersecurity is a foundation for the long term, not a fix. Yet an SME, short of time, resources and guidance, fixes things after the fact. That is the gap I chose to fill.
I start from your operational reality to identify the risks that really matter and help you act, within your means.
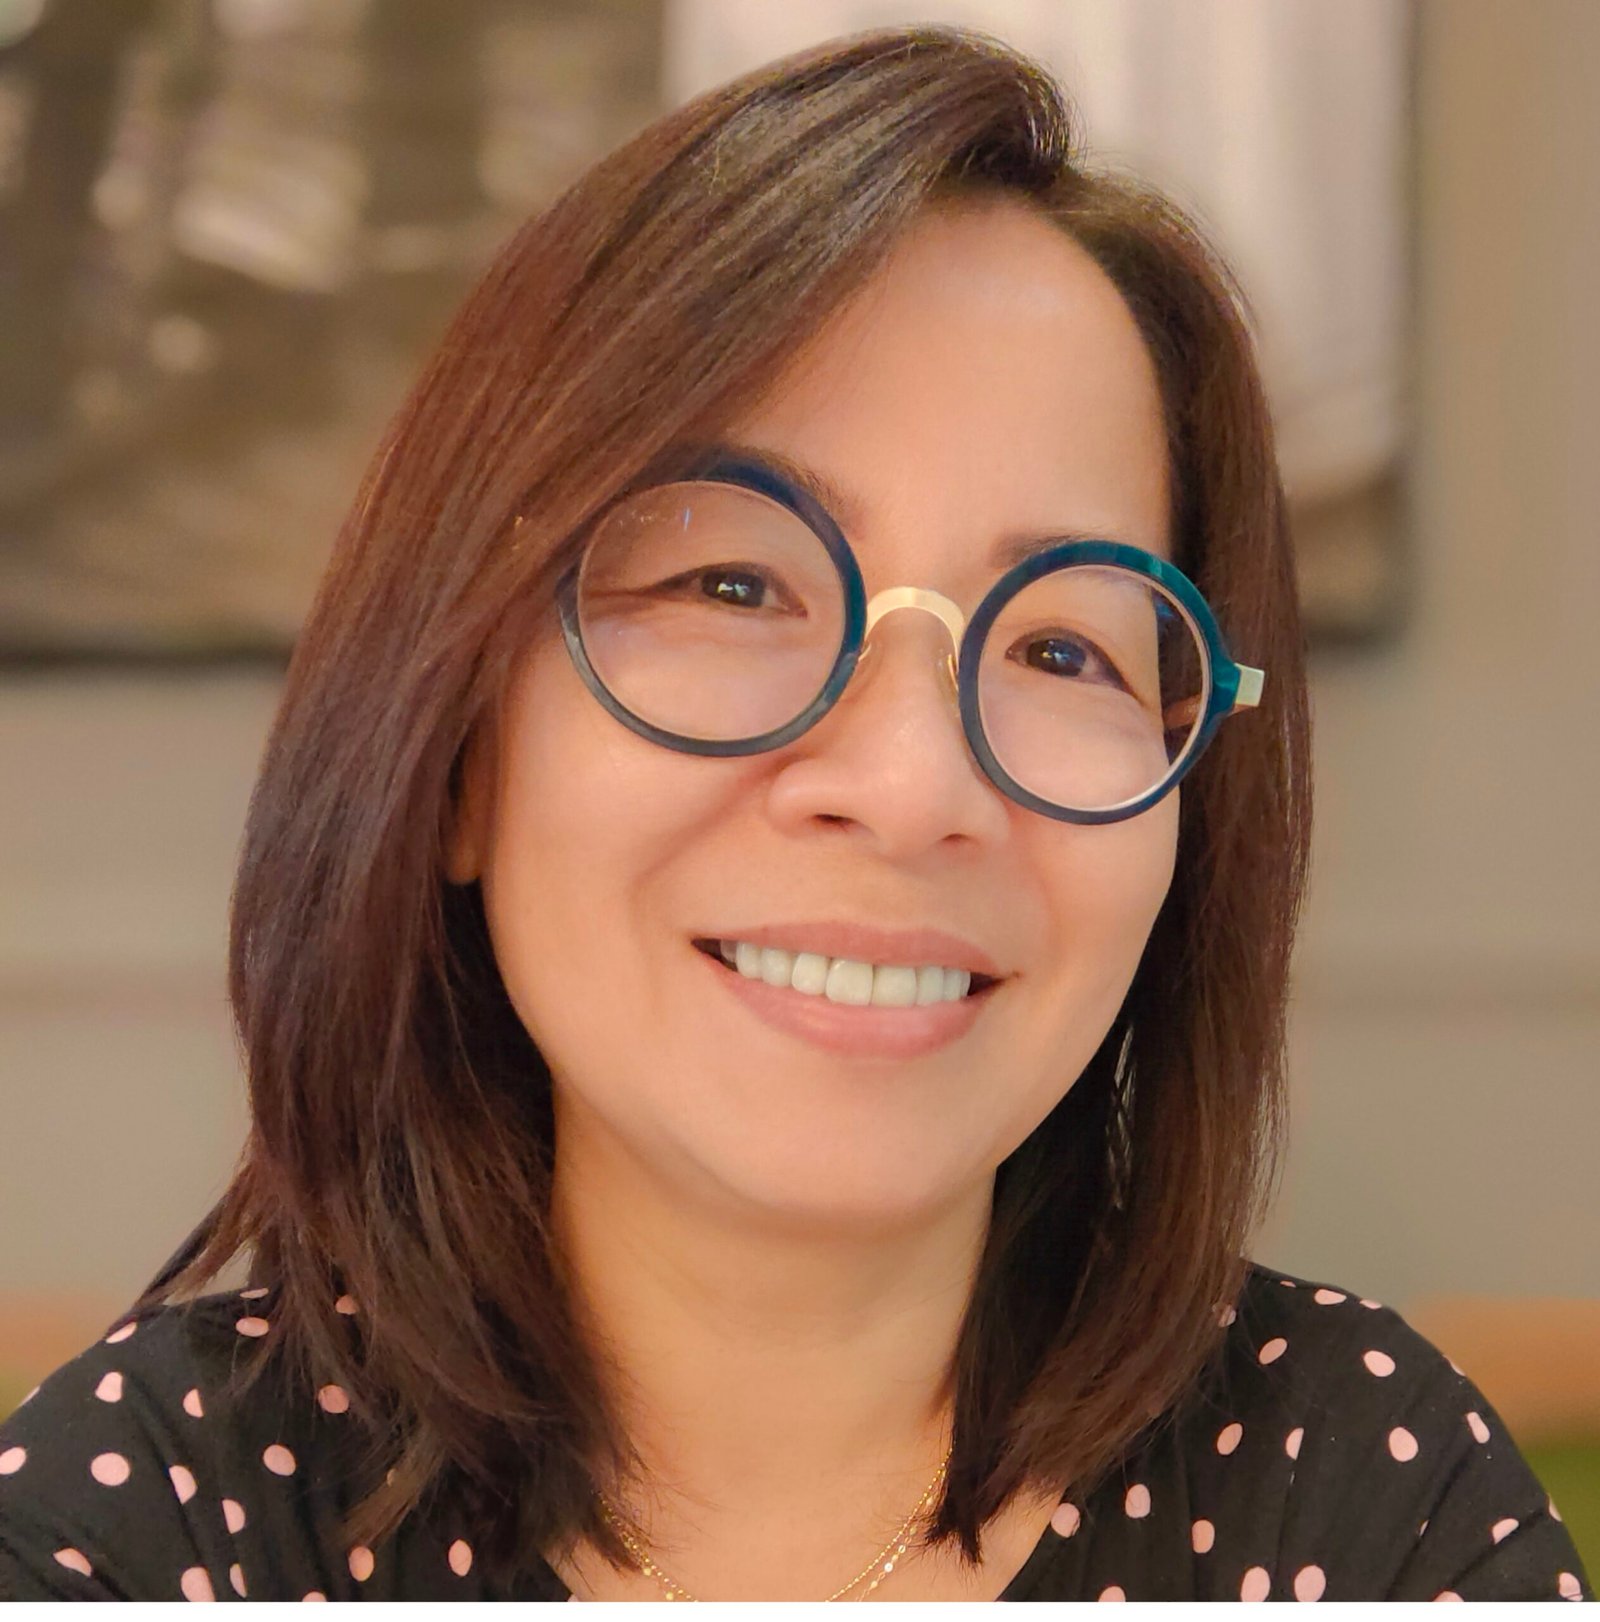
Lai Ly
Cyber Governance Specialist
I spent more than 25 years in international finance, one of the most heavily regulated sectors.
At S&P Global and Amundi, I led credit and ESG risk analysis teams.
I have both assessed and practised governance, the G in ESG. I can tell what really works from what only exists on paper.
Faced with a new risk, I often had to build the method to analyse it. Cyber risk now poses that challenge to SMEs : their clients are already assessing their ability to respond, yet they rarely have the dedicated teams of large corporations.
That is where I come in. I make cyber and regulatory requirements understandable and workable, with the rigour of a large corporation but without the overhead.
With us, your cybersecurity is in the hands of senior specialists.
How we support you
An assessment first. The rest, only if it serves you.
Every company is different.
So is the support you get.
01
SME Cyber Assessment
Aligned with the ReCyF, the NIS2 framework published by ANSSI, France’s national cybersecurity agency, in March 2026.
You know where you stand. You receive :
- an analysis of your cyber risks, across your whole business ;
- a measure of your gaps against the ReCyF ;
- a detailed roadmap to decide on.
Targeted interviews and an on-site visit, without disrupting your business.
02
Implementation
We help you roll out your roadmap, module by module :
- Secure : an action plan proportionate to your business.
- Handle incidents : your teams know how to detect, contain and recover.
- Prove : you answer clients, partners and authorities, with evidence to back it up.
- Steer : everyone knows their role, and the rules are written down.
03
Ongoing support
You maintain your level over time : regular progress reviews, and our assistance if an incident occurs.
Our fees are fixed,
and agreed with you before any commitment.
Our insights
NIS2 and SME cyber : the text, the field, without the drama.
Practical guide · in French
NIS2 and SMEs : a practical guide for business leaders
Are you in scope, what must you do, what do you risk : the text’s answers, situation by situation.
Lai Ly and Stéphane Hivert · updated October 2026
NIS2 and SMEs #1 · in French
Management accountability : what the text actually says
Fines, bans from management : what the Directive really requires of you, and what it does not.
Lai Ly · updated October 2026
Field survey
Cybersecurity in manufacturing SMEs : 3 blind spots revealed by our survey
25 out of 30 business leaders don’t know what NIS2 contains. What we found on the ground, and how to respond.
Stéphane Hivert · 30 SMEs surveyed in March 2026
What sets us apart
Three reasons to work with LINARIS
From one business leader to another
Not cyber theorists. We have faced your constraints ourselves, as business leaders. Our recommendations are concrete and workable.
No hidden sales agenda
Advice, not a catalogue. Our recommendations serve your business, and everything is on the table from the first conversation.
A method aligned with ANSSI
The ReCyF, France’s NIS2 framework, not an in-house method. Choices you can defend to a client, an auditor or an insurer.
An independent view, the rigour of ANSSI, the experience of business leaders.
FAQ
Frequently asked questions : SME cybersecurity and NIS2
How does the free 45-minute session work ?
It is a remote conversation with a LINARIS specialist. We go over your business, your organisation and your main digital dependencies. We also review how prepared you are in cybersecurity for the requirements of your clients, your insurer or NIS2, depending on your situation.
You receive a written summary of the conversation, with an initial estimate of your level of readiness and your priorities.
It is free and with no commitment. The SME Cyber Assessment is a separate engagement, which we only offer if it is useful to you.
You are not lawyers. How do you help me respond to cybersecurity questionnaires or my client’s cyber clause ?
We help you understand exactly what your clients require in cybersecurity, particularly in supplier security questionnaires, identify your gaps and priority actions, then prepare consistent, well-supported answers.
To assess the legal implications of a questionnaire answer that binds you, or of a cyber clause, we recommend consulting your lawyer.
My company is not subject to NIS2. Why prepare for it ?
Because the NIS2 Directive is becoming the market benchmark for cybersecurity. Organisations subject to it must secure their supply chain and may pass their cyber requirements on to their suppliers.
If you supply a client that is subject to NIS2, you may therefore be indirectly affected by its requirements. If not, you are outside its scope for now. But if you plan to expand into a sector covered by NIS2 or to work with a client subject to the Directive, it is wise to get ahead by aligning your cybersecurity practices with the relevant requirements.
What is the difference between my IT service provider and a cybersecurity consultancy ?
We bring a specialised, independent perspective on SME cybersecurity, complementing that of your IT service provider or IT department.
They look after the day-to-day performance, availability and maintenance of your information systems. We assess cyber risks across your whole business and help you define the right measures and steer their implementation.
We help you steer the protection of your business and coordinate all the teams involved, not just IT.
Both areas of expertise are essential, complementary and independent of each other.
Can I handle NIS2 compliance on my own, with software ?
Software helps document and track the large amount of complex information a NIS2 compliance project involves, and we use such tools ourselves. But NIS2 compliance is not just about filling in a questionnaire. You have to decide on priorities, get your teams on board and implement the necessary measures.
Software can also encourage self-assessment, with the risk of lacking perspective and over- or under-investing in cybersecurity.
LINARIS supports your NIS2 project by providing that outside perspective, to rank priorities, inform decisions and coordinate actions.
Do I need technical knowledge to work with you ?
No. Our cybersecurity support engagements are designed for SME leaders, and we speak in management terms, not technical ones. Some steps may call for occasional technical discussions with your IT manager or IT service provider.
We speak several languages : those of senior management, technical cybersecurity and organisation. We bridge these worlds so that everyone understands what is at stake and can contribute.
We help management structure and coordinate the project, without taking over its leadership role.
Will a cybersecurity assessment disrupt my business ?
No. Our approach relies mainly on targeted interviews, an on-site visit and a review of your existing practices. It is designed to fit entirely around your operations.
How much does a cybersecurity assessment cost for an SME ?
The price of a cybersecurity assessment (or audit) depends on the size of your company, the complexity of your activities and of your information system, and how urgent your needs are. You receive a clear quote before any work begins, with no hidden costs.
Contact
Book your free 45-minute situation review
Open the calendar
Calendar not showing ? Call +33 9 85 00 19 31.
Anything else ?
Send us a message
Or call us, we reply within one business day : +33 9 85 00 19 31
Cyber incident : +33 6 56 68 17 11
We call you back within one business day, then step in as quickly as possible in the Paris region : analysis, containment, recovery.
Attack in progress ? First steps on 17Cyber.gouv.fr, the French government’s cyber emergency service (in French).
LINARIS · SME cybersecurity consultancy · Based in Versailles · Serving Paris, the Île-de-France region and all of France · On-site and remote.